Logging into a private account at Bizzo Casino entails more than simply providing a username and password set bizzo.com.nl. Every successful authentication try, unsuccessful login, password reset, and important account change is systematically recorded on the platform’s backend. Understanding how to view and interpret the login history and activity log functions as a foundational practice for maintaining strict account hygiene. This record offers a open audit trail that enables users to verify that no illegitimate party has sought to breach their login details or alter their ongoing session while real-money balances and private personal data remain secured behind the platform’s encryption protocols.
Creating Your Bizzo Casino Account Securely
The path toward a thorough activity log starts with a meticulously completed registration. A fresh registrant should click the sign-up button and supply correct personal information such as a full legal name, a valid email address, and a mobile phone number. The system cross-references this data during the initial validation phase. Submitting falsified details during this step will inevitably create friction later when the withdrawal team demands identity verification documents. A unique password combining uppercase letters, numeric values, and special characters must be generated to establish the first marker in what will become a detailed historical record of account interactions tracked by the server.
Upon submitting the registration form, the platform sends a verification link or a one-time code to the supplied contact channel. Verifying the account through this confirmation step is required and functions as the first manual approval in the user’s lifecycle timeline. Without opening the activation email, the profile persists in a suspended state and is unable to accept deposits. This initial handshake verifies that the email address is associated with the user and captures the exact timestamp of confirmation. Completing this step seeds the nascent activity log with the registration IP address, device type, and browser fingerprint, building a baseline profile for future security correlation checks.
Deciphering the Dashboard Activity Stream
Within the account cabinet, the activity log is displayed as a chronological stream of events, not as a static unchangeable list. Each row constitutes a discrete action and carries a precise UTC timestamp down to the second, a classification tag, and a truncated IP address for privacy compliance. The interface permits a player to filter the feed by date range or by specific action categories. Users watching their security posture closely can isolate “Authentication” events to see every login attempt from the last thirty days. This tool eradicates the guesswork often associated with shared devices or public Wi-Fi usage and brings total transparency.
An entry marked “Login Successful” logs the browser version and operating system. If a rival entry appears marked “Login Failed” with an unrecognized geographic indicator, the account holder gets an immediate signal that a credential-stuffing bot may be targeting their email. The log also records sensitive administrative actions such as updating a linked phone number or modifying the primary email. Any alteration to the account’s fundamental identity structure is permanently inscribed here, providing a forensic trail. Regularly scanning this stream converts a passive user into an active guardian of their own digital funds and personal data integrity.
Configuring Two-Factor Authentication for Improved Log Integrity
Two-factor authentication adds a cryptographic time-based one-time password layer that significantly changes how login history entries are recorded. Activating this feature within the safety settings compels the server to demand a secondary token after the primary password validates successfully. The activity log then captures a two-stage event chain, where a correct password but a missing or late token generates an “Incomplete 2FA” flag. This distinction is critical because it proves the primary credential was exposed yet the secondary barrier remained intact, giving the genuine owner time to rotate the password before a full perimeter breach occurs.
Setting up two-factor authentication involves scanning a QR code with an authenticator application or enrolling a hardware security key. Once enabled, the login log will show a lock icon next to authenticated sessions, verifying the session was protected. A user can review past entries to ensure no session bypassed the second factor. In the rare event of a phone theft or authenticator app failure, the stored backup recovery codes become the primary override method. The consumption of any single backup code is logged as a high-severity event in the log, permanently noting the exact date and time the emergency recovery channel was utilized.
Using the Login Interface Effectively
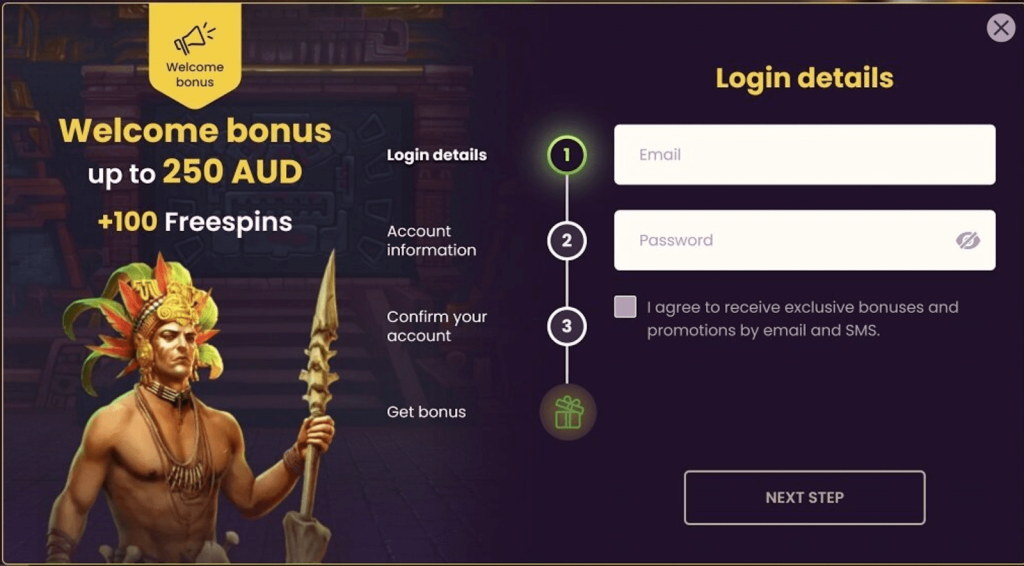
The sign-in portal is crafted with a simple aesthetic to reduce cognitive load, presenting only the essential email and password fields on the primary interface. A user revisiting to the site should manually type the destination URL or use a bookmarked bookmark to avoid phishing domains that mimic the branding. Once the credentials are entered, the system generates a cryptographic hash of the password to compare against the stored database record without transmitting the secret in plain text. The interface includes a toggle option to display the typed password, a tool useful for mobile users whose keyboards may create capitalization errors. Successful authentication unlocks the entry to the personal cabinet.
Directly below the form fields, a “Forgot Password” recovery link is positioned. If a session times out because of prolonged inactivity, the system routes automatically back to this portal, requiring a fresh sign-in. The login page also recognizes whether a user is connecting from a formerly recognized device. If the digital fingerprint is new, an adaptive risk engine may initiate an additional verification step before allowing entry. This silent analysis happens within milliseconds and directly inserts a device recognition entry into the activity log, marking the event as a routine authentication or a high-risk anomaly deserving reviewing later.
Observing Device and Session History
Beyond the chronological event stream, a dedicated session management panel displays currently active and recently terminated sessions. Each logged-in instance holds a descriptive label specifying the device model, the browser engine, and the approximate location based on network mapping. If a user logs in from a desktop in Amsterdam and later spots a concurrent mobile session active from a different continent, the timeline uncovers the intrusion instantly. The interface offers a one-click termination button to remotely log out a suspicious session. Terminating a rogue session instantly revokes the authentication token, forcing the intruder to re-authenticate, a feat impossible without the updated credentials or second factor.
An exhaustive list of previously authorized devices exists within this module. Users often grant “Remember This Device” permission on personal laptops, thereby adding a persistent token to the system. The activity log records each remembered device’s creation date and last use. If a device is lost or sold, removing its trusted status from this panel revokes the stored token without requiring a full password reset. This granular control extends the security perimeter beyond mere password strength. By cross-referencing the device list with the login log, a player can determine whether an old, forgotten tablet still holds an active authorization key to the account.
Confirming Account Documentation and Identity Checks
The Know Your Customer procedure integrates tightly with the activity timeline, leaving audit entries that a careful user can track. When a withdrawal initiates a verification request, the system prompts an upload for a government-issued photo ID, a recent utility bill, and potentially a front-and-back photograph of the payment card used for deposits. Each upload attempt is recorded whether approved or rejected. A rejection entry in the activity feed clarifies the precise reason, such as a blurry image or an expired document, allowing the user to rectify the issue swiftly. Absence of these log entries indicates the documentation queue has not yet been processed.
A fully verified account status grants unrestricted access to the cashier. The log records a “Documents Approved” milestone, effectively upgrading the trust tier internally. From this point forward, any request to change the registered home address requires a fresh re-verification, a change that itself is logged and flagged for manual compliance review. For players who value transparency, this integration means that the status of a payment hold is never a mystery. They can see precisely where they are in the verification pipeline. The immutable nature of these compliance logs safeguards both the operator and the user in case of future disputes.
Reviewing Financial Transactions In the Log
The activity tracker reaches its reach deep into the cashier module, https://www.nieuwsblad.be/cnt/dmf20210822_97504560 efficiently merging security events with financial state changes. A deposit request initiated via iDEAL or an e-wallet produces a pending transaction marker. When the funds settle and become available in the casino wallet, the log logs a success event accompanied by a unique transaction hash. Should a deposit timeout or fail due to insufficient bank balance, a distinct failure entry appears. This granularity assures that a player never needs to chase support for a basic status update. The answer to where funds are located is always shown clearly in the chronological feed for immediate reference.
Withdrawal requests experience an even more detailed documentation process. The log stores the request submission, the internal queue position, the compliance review outcome, the payment processing timestamp, and the final completion notice. Any cancellation of a pending withdrawal by the player while it is in the reversible queue also obtains its own log line. This transparency eliminates the anxiety often associated with waiting for payouts. By scrolling through the transaction history alongside the login history, an account holder can connect large payouts with specific session timestamps, verifying that no financial action occurred outside of their remembered active login sessions.
Maintaining a routine of reviewing the login history and activity log transforms account maintenance into a proactive defense mechanism rather than a reactive scramble after noticing missing funds. The wealth of timestamped data, from registration verification through two-factor challenges to final withdrawal settlements, provides a full narrative of account ownership. Bizzo Casino supplies the instrumentation necessary to audit every digital interaction, and the vigilant player who leverages these tools creates a fortress-like posture around their entertainment budget. Reading the log quarterly, if not monthly, stays a minimal investment for maximum account integrity.
Leave a Reply